Make governed MCP access the default
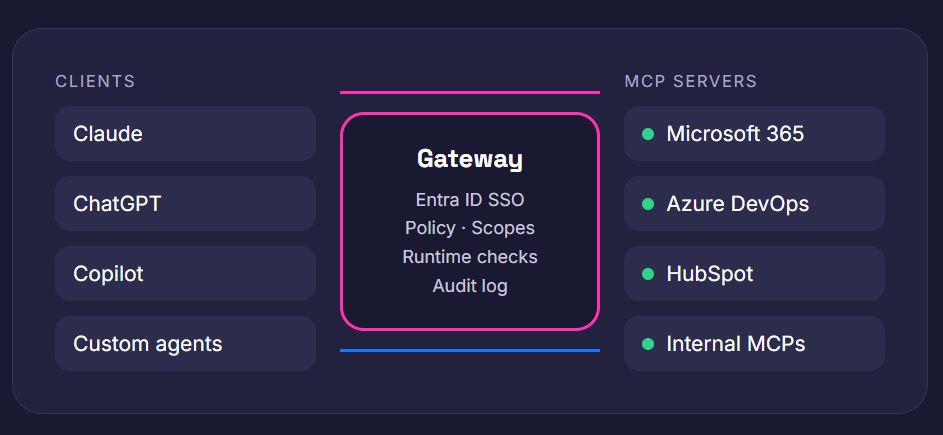
Outerlimit offers a highly scalable gateway for AI clients: Claude, ChatGPT, Copilot, Cursor plus bespoke agents and every MCP server they touch. The Gateway enforces policy and identity in runtime with a full audit trail.
Secure MCP
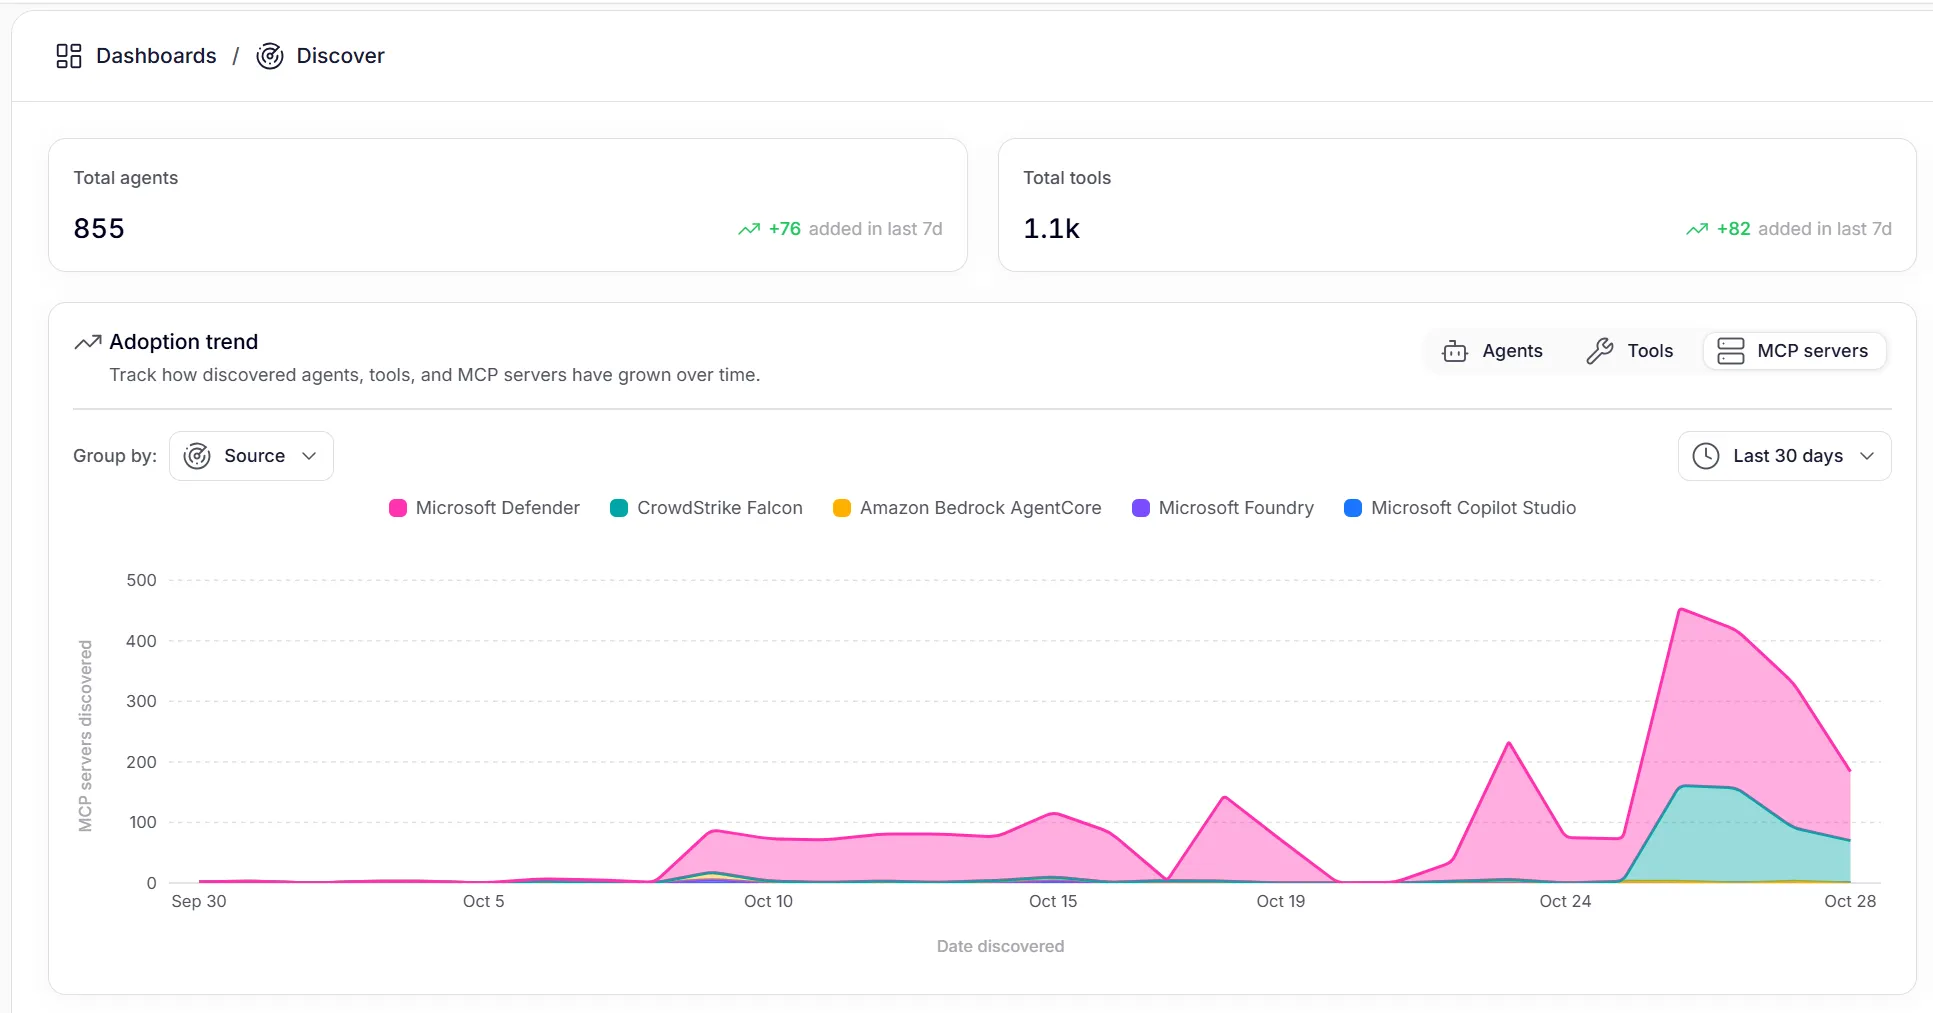
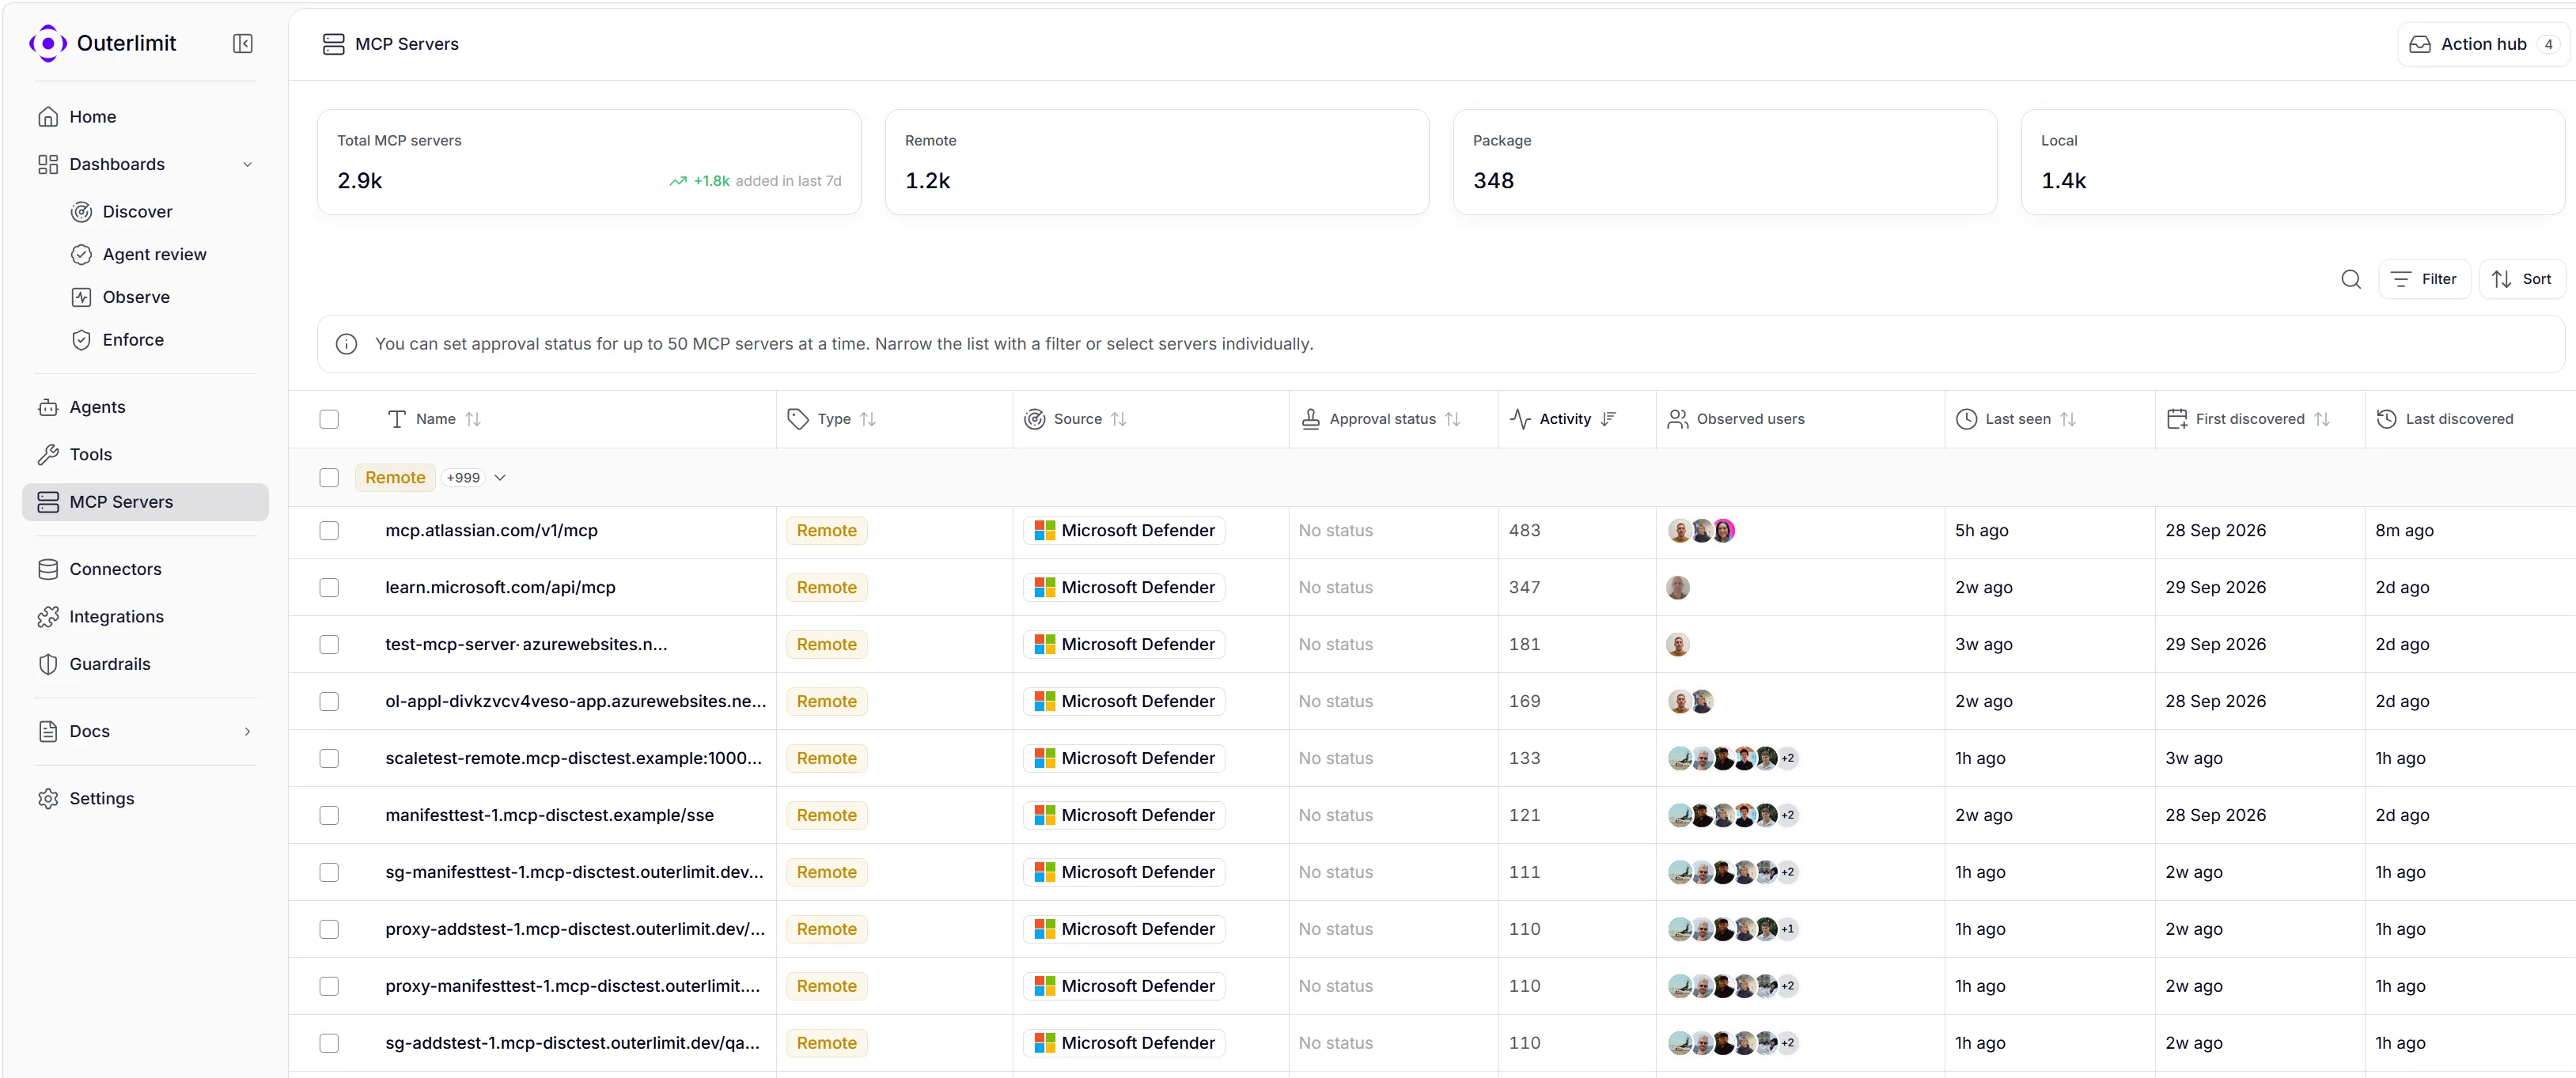
The MCP protocol is now the defacto standard for agentic AI platforms. The challenge all organizations now have is the protocols wide adoption means businesses have no management or control over the use of Local, Remote or Packaged MCP Servers. Outerlimit provides a complete solution for the use of MCP, starting at discovery of every MCP within your estate including internal and external connections. See which MCP servers have been configured, which agents use them and which tools they expose.
Understand your MCP supply chain risks including permissions, exposed secrets/credentials and your overall data security exposure.
Malicious Actions
MCP is a vehicle used by hackers. MCP servers and agent skills can change after they are configured. Attackers can hide suspicious, biased and malicious instructions into tool code, descriptions and skills that AI agents may connect to without the user ever being aware.
These malicious workflows from tools and connected systems can be used to manipulate how the agent acts and be used for actions such as data exfiltration or bypassing system guardrails.
Outerlimit offers governance and enforcement over what is permitted across an organization. Your compliance, security and governance teams now have perfect visibility and control over the MCP protocol.
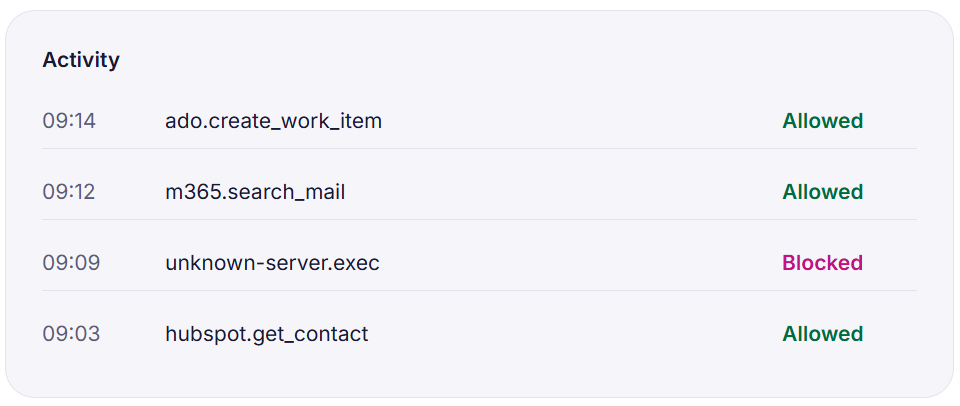
Catalog scanning: stop threats before they are delivered
Outerlimit reads every tool definition before your model does. Each finding comes with a severity, the evidence and a suggested mitigation. These include:
Hidden instructions
Text in a tool that tells the model to skip confirmations, read secrets or keep steps from the user. This includes invisible characters and encoded payloads.
Cross-server interference
One server changing how your model uses another’s tools, or copying a trusted tool’s name to intercept its requests.
Data exfiltration and leaks
Tools or schemas that ask for secrets, send data to hard-coded destinations, or combine to read data and send it out.
Misleading definitions
Tools that claim to be read-only but change data. Destructive tools marked read-only skip the user’s confirmation prompt.
Changes after approval
If an approved tool’s definition changes, it is re-scanned and any finding you dismissed reopens. Anything the scan can’t settle on is sent to a person for review. Nothing suspicious or malicious is approved by default.
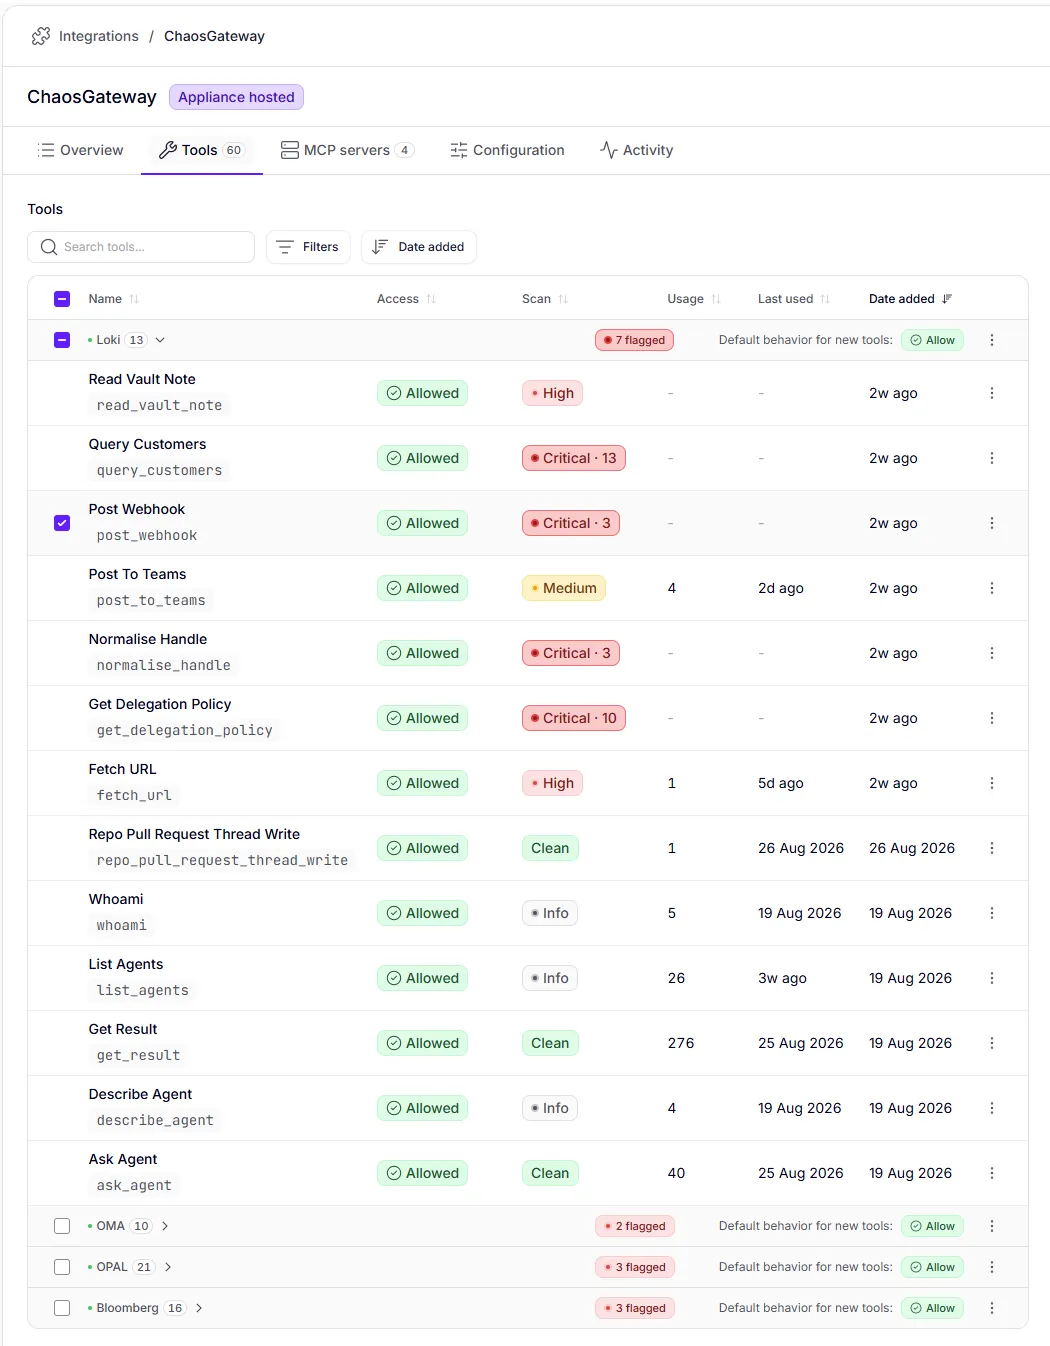
Define approved MCP capabilities
Create and manage a central catalog of sanctioned MCP servers and connectors. Developers and engineers can seamlessly integrate with an approved list of MCP servers and tools restricting the use of unsanctioned or high risk ones.
Approve, review or block new MCP servers either automatically with a defined workflow or manually as part of a governance framework. Tool access can also be restricted with the ability to block all new tools until an authorization process has been completed. Policies can be defined based on group membership with ability to automatically block, allow or permit read only access.
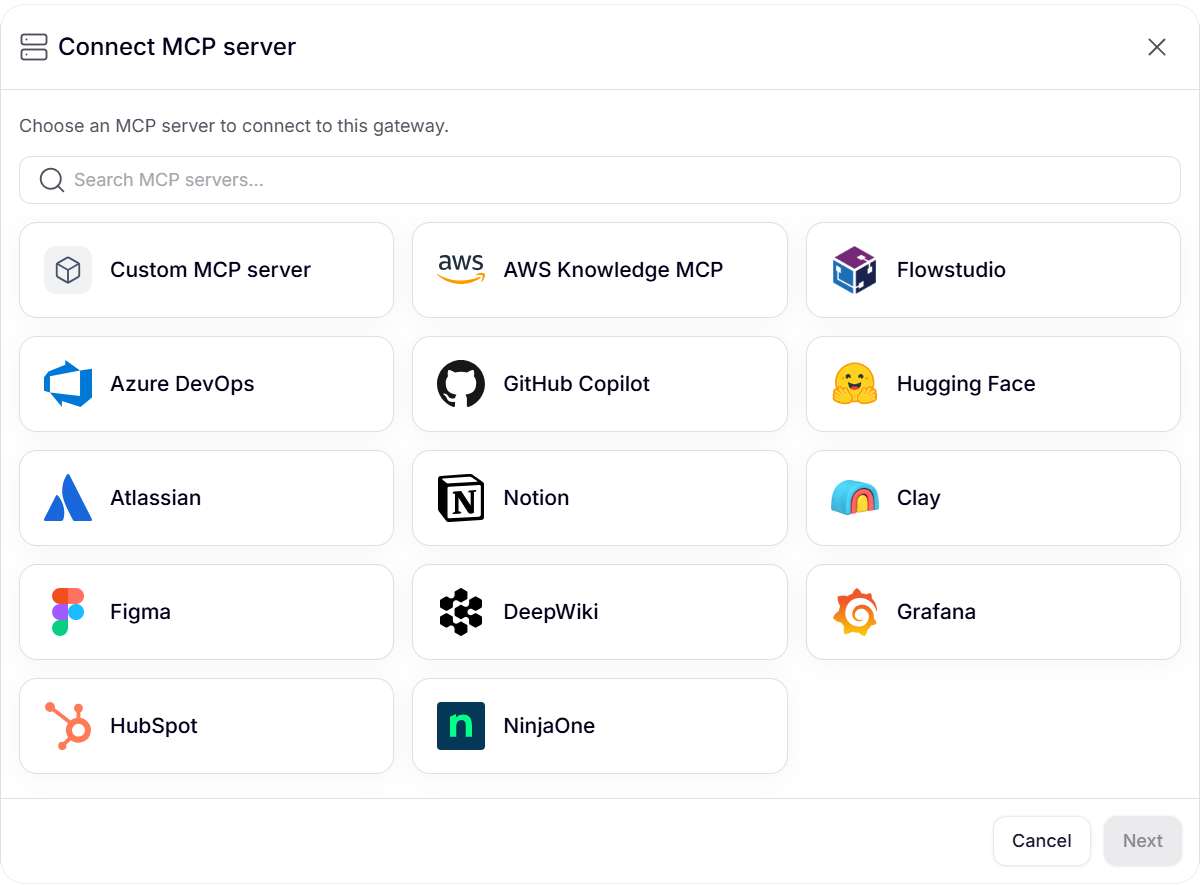
Manage access and identity
You can’t govern what you haven’t found. Outerlimit’s discovery connector scans across Microsoft, AWS, Anthropic and CrowdStrike estates. It creates catalogues of agents, tools and MCP servers as they surface, including local and remote servers spun up by developers that never crossed a changeboard. All of this is done transparently via API connectors and does not require the deployment of an endpoint agent.
Features & Benefits
Build with us. Win with us.
The agentic AI opportunity is not limited to the enterprise. For partners, rapid AI adoption brings with it significant risk, which needs to be addressed. As the market consolidates, channel partners need to align with innovators and category leaders in agentic AI security.
Whether you're a valued-added-reseller, systems integrator or technology vendor, Outerlimit's Partner Program is designed to grow with you and deliver value to our shared customers.